Every vendor.
One control plane.
FreeSDN sits in front of the switches, firewalls, cameras, phones, hypervisors and storage you already run, and gives your team one console, one typed API and one credential vault.
- 13 vendor adapters
- 10 modules
- Self-hosted
- AGPL-3.0
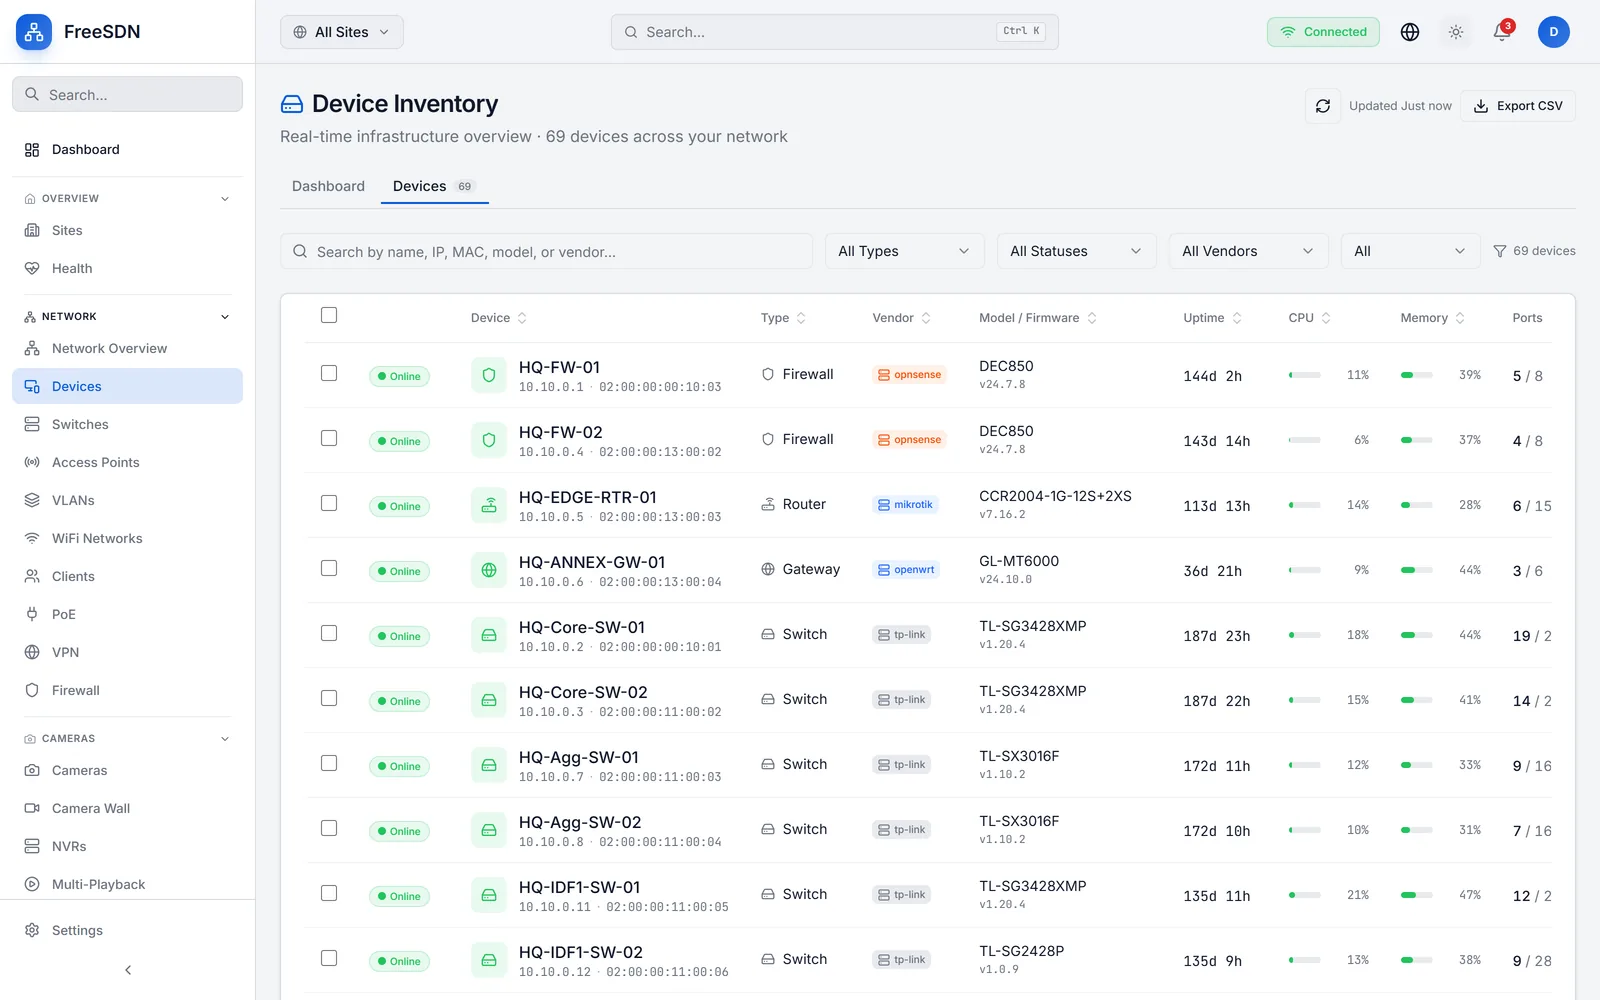
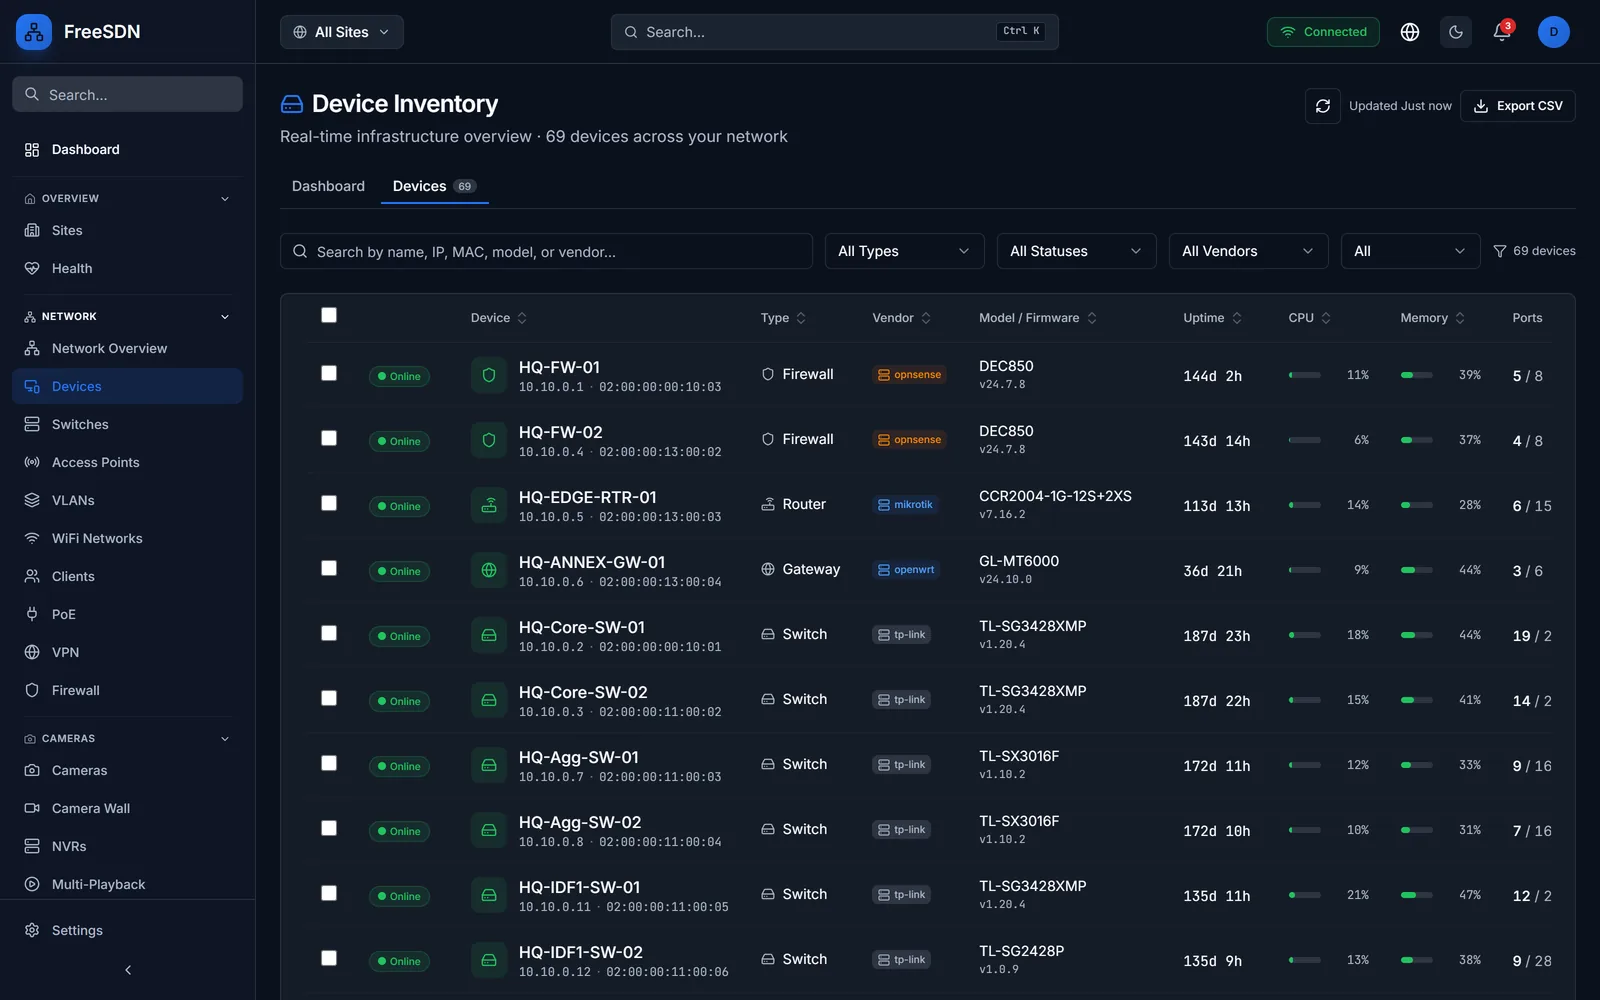
One model in front of every vendor's API
You keep the equipment and the controllers you have. FreeSDN talks to each of them in its own language and gives everything above it a single, consistent way in.
Switching and Wi-Fi
Omada · UniFi · RouterOS · OpenWrt
Firewalls
OPNsense · pfSense
Cameras and NVRs
Hikvision · ONVIF
Phones and PBX
FreePBX · Grandstream
Hypervisors
Proxmox VE
Storage
TrueNAS
- Adapters13 adapters, each speaking its vendor's own API
- Data modelSites, devices, clients and alerts in one shape for every vendor
- Credential vaultEncrypted at rest, and redacted from adapter data before it leaves the API
- Change stagingA write waits for the platform switch and an operator's explicit apply
- Audit logPrivileged actions recorded with before-and-after values
Web console
Scoped to the sites each person is granted
REST API
1,887 typed routes, with an OpenAPI spec
Automation
Event subscriptions, scheduled plugins and a typed SDK
10 modules. One console.
Turn on what each organization needs. Every module shares the same sites, roles, credential vault, audit log and API, so adding a camera estate does not mean adding another tool.
Built for teams who answer for every change
Network changes break things. FreeSDN is designed so that every one of them is deliberate, scoped to the right people, and on the record.
Staged writes behind two gates
No change reaches a device from a single click. Every adapter write is staged first, and is applied only when the platform allows writes and an operator explicitly confirms it.
Roles and per-site grants
Five assignable roles, and nobody can grant a role at or above their own. Per-user site grants then narrow each person to the sites they actually run.
An audit trail of every privileged action
Who did what, to which resource, with the values before and after. The record is there when a change has to be explained.
Credentials that stay sealed
Device credentials are encrypted at rest, and around 120 secret-bearing keys are redacted from adapter data before any response leaves the API.
A signed supply chain
Plugin catalog entries are Ed25519-signed and unsigned packages are refused by default. Every shipped image is scanned before a release goes out.
Maturity it has to earn
Each integration states separately whether its reads and its writes are proven on real hardware, and a CI check stops the product from claiming more than it has recorded.
Green on the exact commit that ships
Since 26.10.4, a release is published only after every check on its own commit has passed on GitHub's runners: the full backend suite, the frontend build, an API contract check, a dependency audit and a vulnerability scan of every shipped image.
Security releases ship monthly, and every change, including what broke, is written down in the changelog.
- 26.11.3Current
Security release
Fixes the four known issues 26.11.2 listed and the problems a code review of the areas around them found: first-run setup needs a one-time code, Lite starts on HTTPS, desk-phone configuration is no longer handed to the whole site network, read-only access and passwords are enforced across VoIP and camera evidence, FreeSDN checks the address it actually connects to, and watermarked and legal-hold exports work and are checked for coverage.
- 26.11.2
nginx and FFmpeg security hotfix
nginx 1.30.7 for the optional nginx web server, which was exposed when it terminates TLS, and for the HA load balancer, after nginx's 2026-11-18 security release, which fixes two HTTP/2 remote code execution flaws; the default Caddy edge is not affected. FFmpeg is now built with only the camera codecs and outputs FreeSDN uses, after 114 FFmpeg advisories. Cameras behind a Hikvision NVR show whether they are online.
- 26.11.1
Safety and reliability
Fixes found on a real multi-site fleet and in a broad code review. Read-only mode now holds everywhere, the backup viewer no longer shows VPN passwords, webhooks deliver, deleted organizations lose access, and polling backs off from struggling devices.
Running on hardware you control
FreeSDN ships as a Docker Compose stack that is built and run entirely on your own machine. Nothing leaves your network, and there is nothing to license.
- 1Clone the repositoryOne repository holds the whole platform, the Compose files for every tier, and the installer.
- 2Run the installerIt checks for Docker and Python, writes a configuration with generated secrets, builds the images on your machine and starts the stack. Choose lite, pro or max, and pass a domain for automatic HTTPS.
- 3Finish in the browserThe first-run wizard creates your admin account, organization and first site, then connects your first controller. There is no default password.
$ git clone https://github.com/freesdn/freesdn.git
$ cd freesdn
$ ./install.sh --tier lite
# a team or several sites:  ./install.sh --tier pro --domain freesdn.example.com
Free, all of it
AGPL-3.0-only
Every module, every adapter and every tier is free to run. No per-device fees, no licence keys, and no feature held back for a paid edition.
- Docker 24+
- Compose v2
- Python 3
- 4 GB RAM
See it running in your browser
Explore the full FreeSDN console on realistic sample data. No signup, no backend, nothing to install.